Phishing Campaign Targeting Nexus Users Identified
Published: 2026-04-25 · ← Back to News
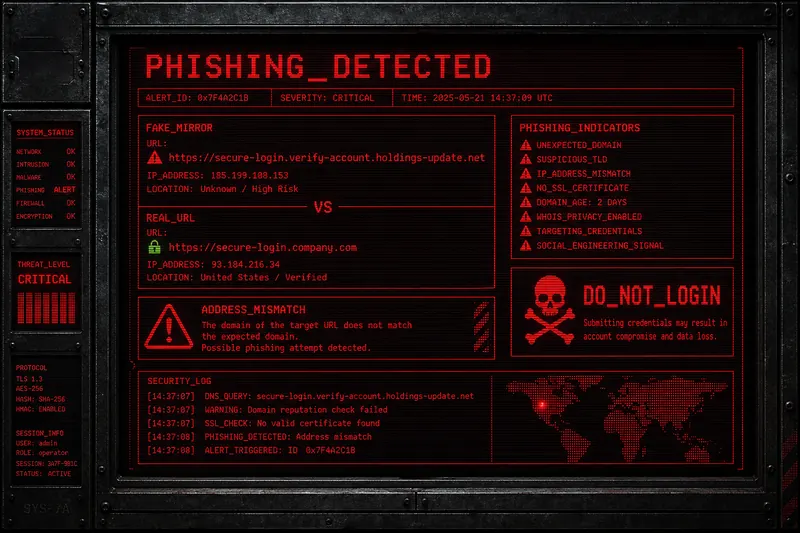
A coordinated phishing campaign deploying fake Nexus onion mirrors has been documented by community security researchers. The campaign uses visually identical replicas of the Nexus interface served from crafted onion addresses that differ from legitimate mirrors by one or two characters — specifically targeting users during period of high traffic or service disruptions.
The phishing infrastructure captures login credentials and displays fake deposit addresses to redirect cryptocurrency payments to attacker-controlled wallets. Affected users have reported account takeovers and loss of escrow funds. The campaign appears to be distributed through fake link lists on clearnet forums and Telegram groups impersonating Nexus update channels.
Protection: Only use onion addresses from verified sources such as the mirrors page on this site. Verify the full 56-character address before logging in. See the full anti-phishing guide for additional protection measures.